Wireshark | pcap
Compatible with:
LRS4000
multiScan100
multiScan200
picoScan100
Packet captures record the raw Ethernet communication between the sensor and a host computer. Use Wireshark, tcpdump, or tshark to capture packets. A capture retains complete raw sensor data for protocol-level diagnostics. It is useful for customer support, network troubleshooting, and protocol decoder development. Captures are saved as .pcap or .pcapng files.
For Compact format captures, use the Wireshark Compact dissector to decode the packets. The Lua plug-in is available at COMPACT_Dissector.lua.
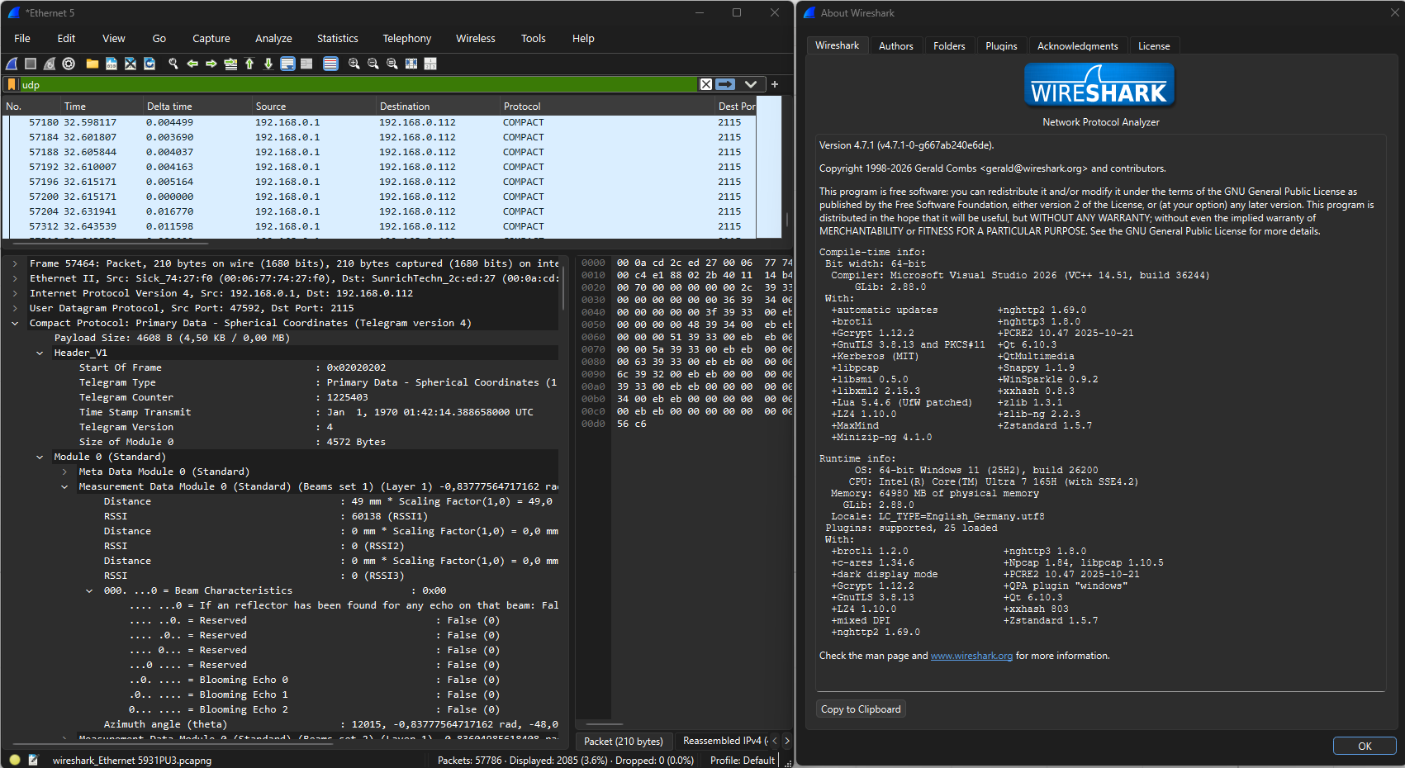
Wireshark displaying decoded Compact measurement data with the SICK dissector.